How to Vet AI Marketing Tools for Privacy Risk
Introduction
An AI marketing tool may promise faster campaign briefs, sharper audience insights, and endless variations of personalized copy. But behind the polished interface sits a more important question: where does your data go, and what can happen to it after you click submit?
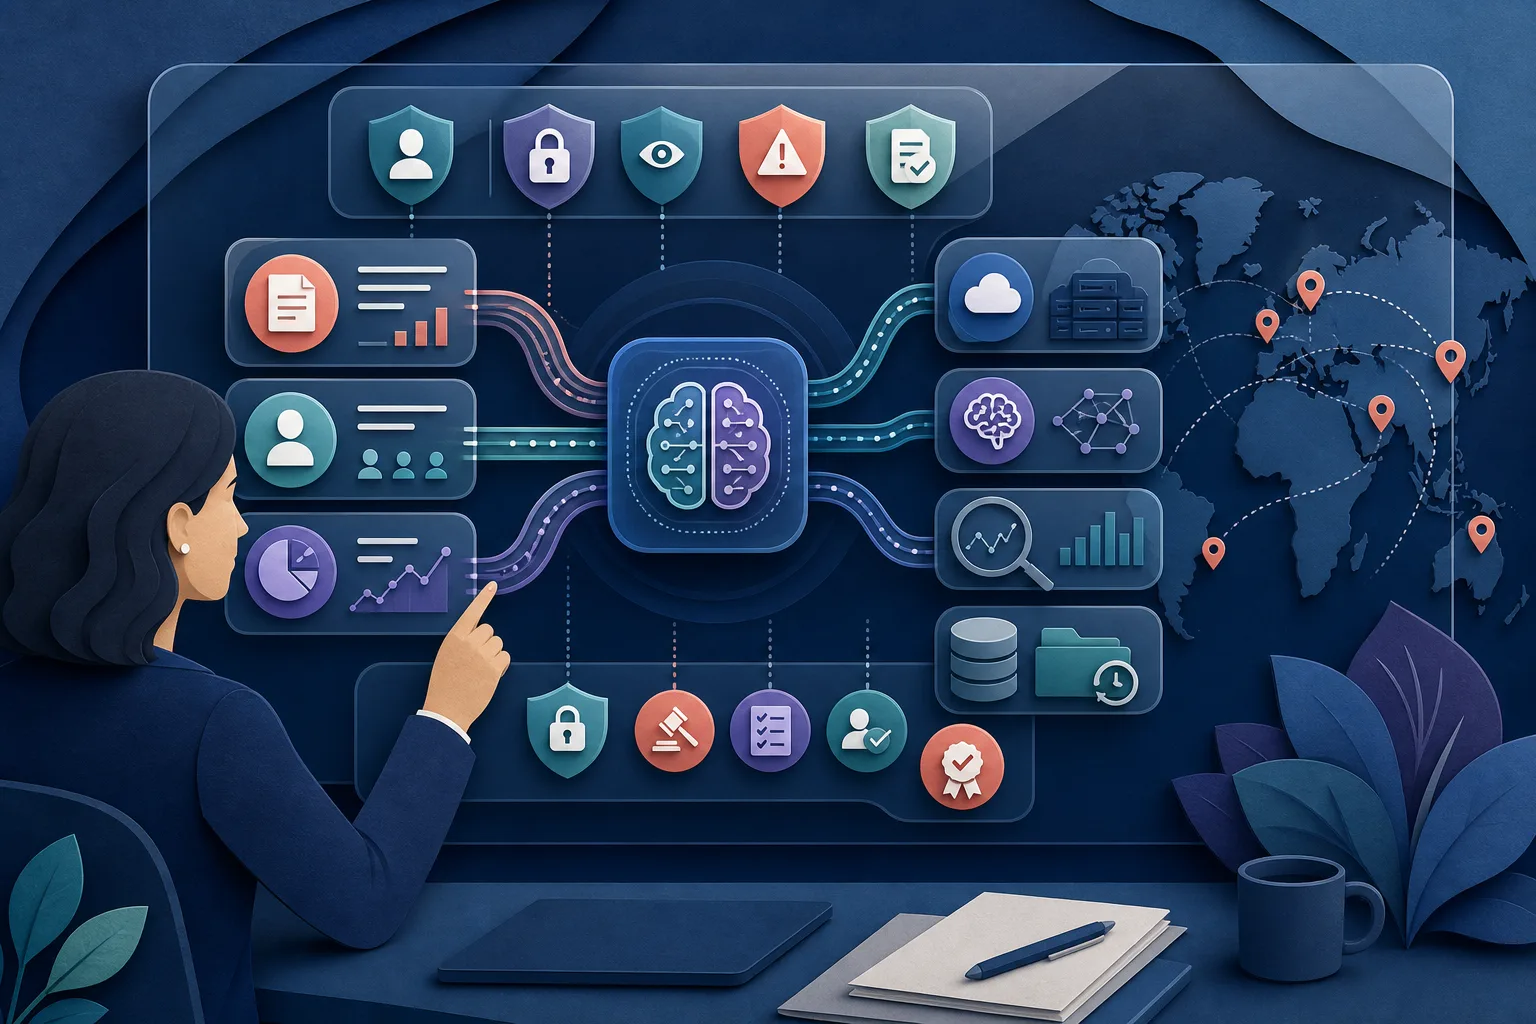
That question is difficult because the visible vendor may be only one part of the system. Prompts could pass through an application provider, a cloud platform, a foundation-model company, monitoring services, and backup systems. Uploaded customer lists, brand documents, campaign results, and generated outputs may each follow different paths.
For marketing teams, this is not merely an information security exercise. A leak could expose unreleased products, pricing plans, audience segments, customer information, or confidential brand strategy. Vetting therefore needs to cover two related risks: data residency, meaning where information is stored or processed, and model leakage, meaning how sensitive information could be retained, exposed, or reproduced through an AI system.
A good review replaces broad assurances with a data-flow map, independent evidence, enforceable contract terms, and ongoing oversight.
Start With the Data, Not the Product Demo
AI due diligence should begin with the information your team intends to provide. A low-risk tool used only to rephrase public website copy is not equivalent to a platform connected to a customer relationship management system, advertising account, or product roadmap.
Create a simple inventory of likely inputs and outputs:
- Campaign briefs, creative concepts, and unpublished messaging
- Customer names, email addresses, purchase histories, or support records
- Audience segments and advertising performance data
- Brand guidelines, research reports, and competitive analysis
- Generated copy, predictions, scores, and recommendations
- User identities, activity logs, prompts, and feedback
Classify these materials according to your organization’s existing rules. If a tool will handle personal data, confidential strategy, regulated information, or valuable intellectual property, it should receive more scrutiny than a standalone writing assistant processing public material.
This step also exposes a common misunderstanding: deleting a conversation from the user interface does not necessarily remove every server log, cached copy, backup, embedding, or record held by a subprocessor. The review must cover the full technical system rather than the screen marketers see.
Ask what the tool can access automatically
An AI assistant connected to Salesforce, HubSpot, Google Drive, or an advertising platform may retrieve much more than a user consciously pastes into a prompt. Determine whether the integration requests broad account access or only the minimum permissions needed.
Look for controls such as role-based access control, single sign-on, multifactor authentication, workspace separation, and detailed audit logs. The tool should respect the permissions of the person making a request rather than turning an AI assistant into a shortcut around existing access rules.
Map Residency Across the Entire Data Flow
A statement such as “EU hosting available” is useful only if it describes every relevant part of the service. Storage may remain in one region while model inference, technical support, telemetry, or backups occur elsewhere.
Request a data-flow map covering:
- Collection: How prompts, files, integrations, and user records enter the service.
- Processing: Where classification, retrieval, generation, filtering, and analytics occur.
- Storage: Where source data, outputs, logs, caches, embeddings, and backups remain.
- Sharing: Which cloud providers, model developers, analytics services, and support vendors receive data.
- Deletion: How information moves out of active systems, archives, and backups.
The map should identify locations and subprocessors, not merely display generic cloud icons. If the vendor uses a third-party large language model, ask which provider processes each feature and whether the selected residency option applies to that provider as well.
Residency is not the same as privacy compliance
Data residency answers a geographic question. It does not, by itself, establish that processing is lawful, secure, or appropriately limited. An organization may still need a valid processing purpose, suitable contractual protections, retention limits, access controls, and procedures for individual privacy rights.
For personal data, examine the vendor’s Data Processing Agreement. Confirm the parties’ roles, permitted purposes, international transfer arrangements, security obligations, assistance with privacy requests, and deletion requirements. Where the processing creates elevated privacy risk, a Data Protection Impact Assessment summary can help the buyer understand how the vendor has evaluated that risk.
The California Consumer Privacy Act and the General Data Protection Regulation create different obligations, so a generic “privacy compliant” label is not enough. Legal and privacy teams should assess the tool against the organization’s actual markets, data subjects, and uses.
Examine network and storage architecture
Higher-control deployments may offer private endpoints, which keep traffic between approved networks and cloud services rather than sending sensitive payloads over the public internet. Encryption should protect information both in transit and at rest, with clear responsibility for managing encryption keys.
Private connectivity reduces one category of exposure, but it does not answer what the provider does after receiving the request. Buyers still need to investigate logging, human access, retention, training, and subprocessors.
Test the Vendor’s Model-Leakage Story
“Your data is secure” is too broad to evaluate. Model leakage includes several different failure paths, and each requires a different control.
Training and memorization
Customer prompts, files, outputs, or feedback could be used to train or improve a shared model. Training creates a concern that proprietary or personal information may influence future behavior outside the original customer’s environment.
Ask for a written commitment that customer data will not be used to train shared or foundation models without explicit authorization. Confirm whether this restriction covers prompts, uploaded files, generated outputs, human feedback, fine-tuning data, and metadata. An opt-out buried in account settings is weaker than a default restriction backed by the contract.
A no-training commitment is important, but it is not the same as zero data retention. A provider may avoid training while still storing requests for abuse monitoring, troubleshooting, or analytics.
Retention and request carryover
Zero data retention generally means that request content is removed after processing rather than kept in provider logs. Buyers should verify exactly what “zero” excludes. Account records, security events, billing metadata, and legally required records may follow separate policies.
Also ask whether interactions are stateless. A stateless request does not carry customer content into later requests unless the application intentionally supplies that context. This reduces accidental cross-session exposure, although it does not replace access controls or deletion rules.
If zero retention is unavailable, require precise answers:
- What content is retained, and for what purpose?
- What is the exact retention period?
- Can administrators shorten it?
- Are deleted records removed from backups, and on what schedule?
- Can authorized personnel inspect prompts or outputs?
Unauthorized access to outputs
Leakage can occur without model training. An employee may see another team’s conversation, an overly powerful connector may retrieve restricted documents, or a compromised account may expose generated audience insights.
Ask whether workspaces and customer tenants are logically isolated. Review identity controls, privileged-access procedures, audit trails, and monitoring. For tools using retrieval-augmented generation, confirm that document retrieval applies the original source permissions before content reaches the model.
Prompt injection also deserves attention. A malicious instruction hidden in a web page, email, or document can attempt to manipulate an AI agent into revealing data or taking an unintended action. Vendors should be able to explain how they isolate untrusted content, restrict tools, enforce policy at the request boundary, and record consequential decisions.
Verify Claims With Evidence and Contract Terms
Security badges are starting points, not conclusions. ISO 27001 certification indicates that an organization operates an information security management system. A SOC 2 Type II report provides independent evidence about how specified controls operated over a period. Neither automatically proves that every AI feature, model provider, or production environment is covered.
Ask to review the underlying evidence under a nondisclosure agreement where appropriate. For a SOC 2 report, examine:
- The legal entity, services, systems, and locations within scope
- The review period and whether the report is current
- Any control exceptions and management’s response
- Complementary controls that customers must operate themselves
- Whether the production AI service and relevant data stores are included
For ISO 27001, inspect the certificate’s scope and validity rather than accepting a logo. Request a recent penetration-test summary and evidence that significant findings were addressed. A current subprocessor list is also essential because an otherwise strong vendor may rely on model or infrastructure providers with different residency and retention terms.
Put operational promises into the contract
A sales presentation can change; a contract creates accountability. The agreement should define:
- Approved storage and processing regions
- Permitted purposes for customer data
- A prohibition on unauthorized model training
- Retention and deletion periods, including termination
- Subprocessor disclosure and change notifications
- Security incident notification requirements
- Access to relevant logs, assurance reports, and incident records
- Audit or inspection rights proportionate to the risk
- Notice of material model, architecture, or residency changes
Do not accept “commercially reasonable” deletion where an exact period is necessary. Likewise, a promise to use “industry-standard security” cannot substitute for named controls and a clear description of responsibilities.
Use risk-based scoring, not a badge count
Score vendors across collection, storage, processing, sharing, residency, retention, access control, incident readiness, and contractual enforceability. Weight the categories according to the use case.
For example, residency and deletion may dominate the assessment of a customer-data platform, while model training and intellectual-property protection may matter most for a creative strategy assistant. A tool should not receive a passing score simply because it holds more certifications than a competitor.
A limited pilot can reduce uncertainty. Use synthetic or public data, disable unnecessary connectors, restrict the user group, and inspect logs before approving production information. The pilot should test governance controls, not just output quality.
Checklist
- Inventory the prompts, files, customer data, outputs, metadata, and integrations the tool will handle.
- Obtain a complete data-flow map showing processing regions, storage locations, model providers, and subprocessors.
- Verify training, retention, deletion, backup, and stateless-request claims in writing.
- Review the scope, dates, exceptions, and production coverage of SOC 2, ISO 27001, and penetration-test evidence.
- Test identity controls, tenant isolation, connector permissions, audit logs, and prompt-injection defenses.
- Place residency, no-training, deletion, incident, audit, and material-change obligations in the contract.
- Assign an owner and reassess after incidents, new subprocessors, certification lapses, major releases, or residency changes.
Frequently Asked Questions
Does EU data residency make an AI marketing tool GDPR compliant?
No. EU residency may support a privacy strategy, but it answers only where certain processing or storage occurs. Compliance also depends on the purpose and legal basis for processing, data minimization, retention, security, contracts, privacy rights, and any international transfers elsewhere in the service chain.
Is a SOC 2 Type II report enough to approve a vendor?
Not by itself. It is useful independent evidence, but buyers must inspect the report’s scope, review period, exceptions, and customer responsibilities. Confirm that the relevant AI product, production environment, data stores, and supporting processes are included.
What is the difference between no training and zero data retention?
A no-training policy means the provider does not use covered customer information to train or improve specified models. Zero data retention addresses whether request content remains after processing. A vendor can offer one without the other, so both claims require separate verification.
Should marketers ever enter customer data into a generative AI tool?
Only when the use is approved, necessary, and supported by appropriate privacy, security, and contractual controls. Teams should minimize the fields supplied, remove identifiers where possible, restrict access, and avoid production data during early testing.
How often should an approved AI vendor be reassessed?
Use a regular review cycle suited to the risk, but do not rely on the calendar alone. A new model provider, subprocessor change, major product release, residency change, certification lapse, or security incident should trigger an earlier review. Assign a named owner and an escalation path so monitoring leads to decisions.
Final Thoughts
In practice, the most revealing artifact is rarely a certificate. It is the data-flow map. Once a buyer can see where prompts, files, outputs, logs, embeddings, and backups travel, vague claims about privacy become testable questions.
The second judgment is that model leakage should be treated as a set of distinct risks rather than one dramatic scenario. Training, retention, excessive access, insecure retrieval, and prompt injection have different causes. A vendor that controls one may remain weak in another.
There is also a real tradeoff between capability and exposure. Deep integrations can make an AI marketing system more useful, but every connector, model provider, and retained context expands the environment that must be governed. The best choice is not necessarily the tool with the most features; it is the one whose access matches the business need and whose behavior can be verified.
Finally, approval should be viewed as a maintained decision rather than a one-time gate. AI services change quickly through new models, subprocessors, and architectures. Marketing teams need procurement discipline that can keep up: named ownership, meaningful change notices, enforceable contracts, and the willingness to pause a deployment when the evidence no longer supports trust.
Sources
- How to Score Data Privacy & Compliance for AI Tools: A GDPR & CCPA‑Ready Checklist
- AI Due Diligence: What Businesses Should Check
- GDPR Compliant AI: 12-Point Checklist for Agents (2026)
- Keep absolute control over your data and still enjoy Generative AI | Rewire | Data & AI Consultancy
- How Does Generative AI Handle Privacy And Data Security
- Generative AI & Data Privacy: What to Look for in an AI Vendor | Regie.ai · Regie.ai
- AI Agent Security: Protect Data & Prevent Breaches in 2026
- The AI Vendor Security Questionnaire: 38 Questions ...
- Email Security Platform Data Residency: Verify Compliance ...
- SOC 2 & ISO 27001 Compliance with AI Audit Trails
- Auditing AI Platforms: SOC 2 Considerations & Guidance
- Vendor SOC 2 Reports: 9 Easy Review Steps + Checklist | Scrut
Ready to Get Started?
Explore production-ready 3D models for your next project. Browse the 3D model catalog to download assets you can use right away.
Turn this workflow into real deliverables
Browse production-ready 3D models for your next project, then step into 3d modeling if you need a custom build.